

Manage group membership in Cognite Data Fusion
To manage group membership for user accounts in Cognite Data Fusion, you can add all authenticated users or individual users to CDF groups. To add individual users, they need to already have signed in to a CDF project. Groups that have All user accounts as members display first in the Groups overview page. To manage membership for service accounts, use your identity provider.Create a group in CDF and add members
1
Sign in to Cognite Data Fusion
Sign in to Cognite Data Fusion as an admin.
2
Create a group
Select the Admin workspace, and then Access management > Groups > Create group.
3
Configure the group
Enter a unique name and add capabilities.
4
Configure group members
Under Members: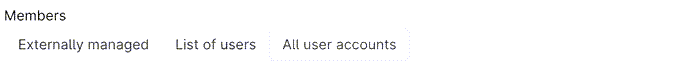
- To add all users of the organization to the group, select All user accounts.
- To add individual users, select List of users and then the users you want to add.
Only profiles of users who have logged into the organization at least once are visible.
5
Link to Application (Client) ID
In the Application (Client) ID dropdown, select the existing or create a new Application (Client) ID to link groups to specific applications to improve query efficiency. Application (Client) ID is a unique public identifier for an application registered with an authorization server. You can set more than one Application (Client) ID for a group.When users make a query to CDF, their Effective Access (EA) is determined by the union of all capabilities and scopes from the groups they’re members of. When users make a query from an application, only the groups linked to that application are considered for EA.
This feature is currently supported only for CDF organizations configured with Microsoft Entra ID as their identity provider (IdP).
6
Select Create
Currently, you can only add user accounts as members of a CDF group. For service accounts you need to create the service accounts in your identity provider and manage their group membership as Externally managed.